Skip to content
COLONFILM

WEBSITE SECURITY / AUTHORIZED ASSESSMENT

WEBSITE SECURITY AUDIT.
Know which findings need attention first.

A scan is useful when your team can understand and act on its findings. Our website vulnerability assessment turns an agreed set of checks into a prioritized report with evidence and remediation recommendations. Choose a website security audit of the public site, a web application security assessment with login, or an app and API review with one retest.

Security assessments from $390 USD

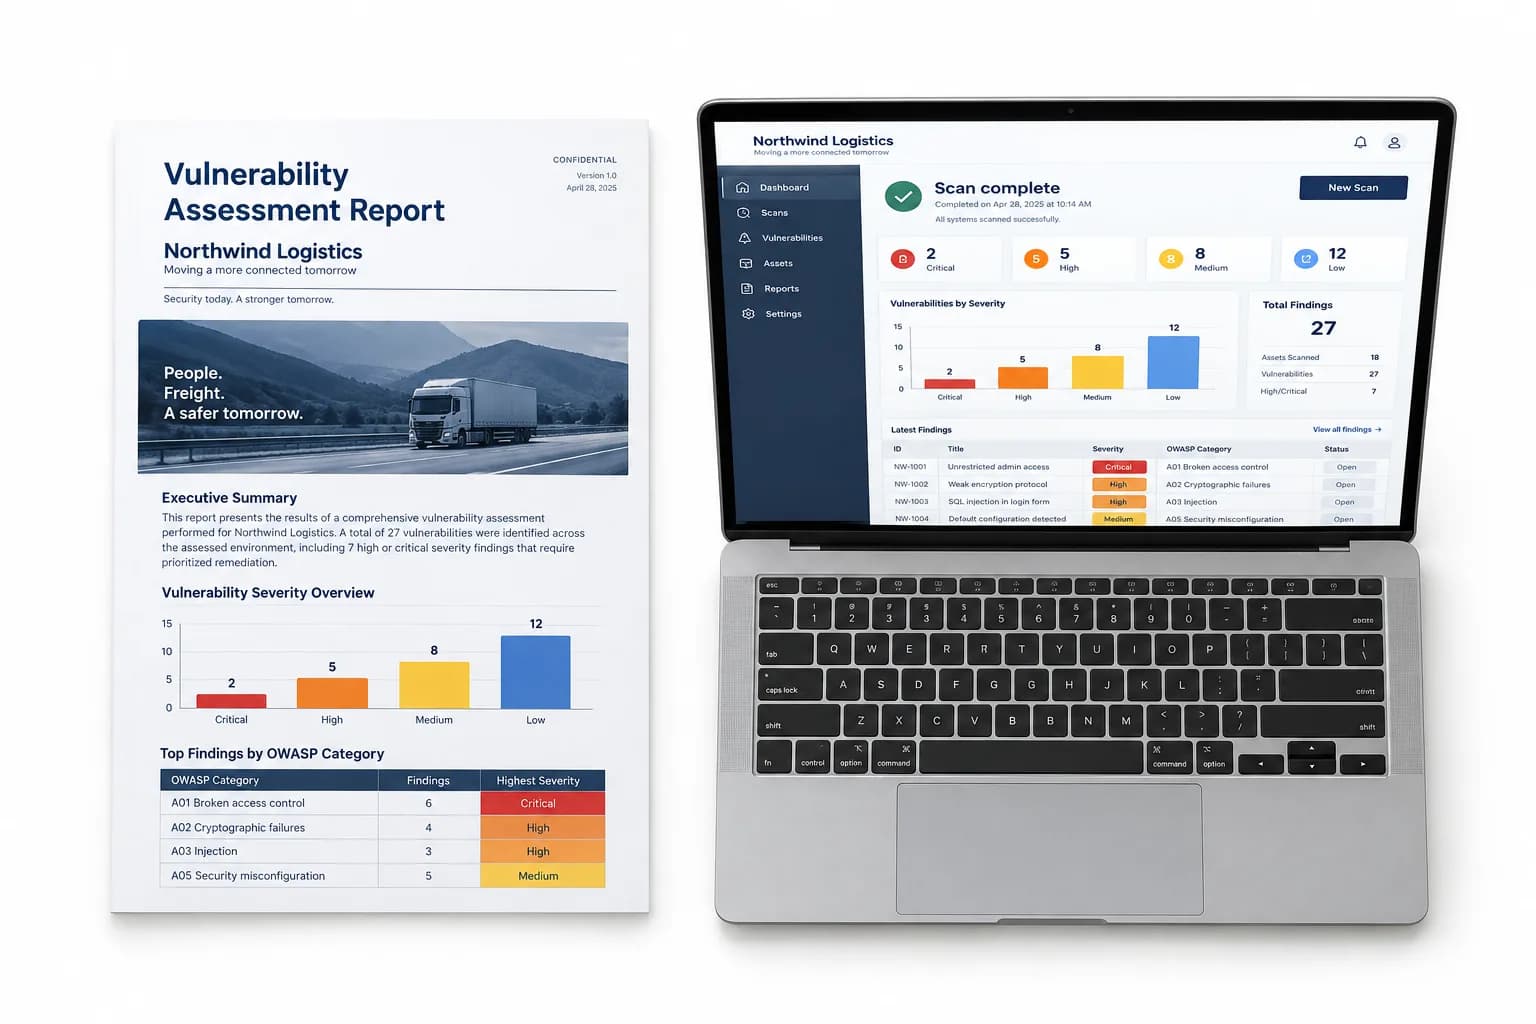
Illustrative AI concept for fictional Northwind Logistics: a navy vulnerability report with severity chart beside a laptop showing scan findings on white.
AI-generated visual concept

01 / Written authorization required

02 / Findings with evidence and priorities

03 / App and API retest in Premium

AI-generated visual concepts to show possible styles, not client projects. Select an image to enlarge it.

DEFINE THE TARGET. Get an assessment your team can use.

Basic scans one public website externally. Standard assesses one application with login and OWASP Top 10 checks. Premium includes the application's API, fixes guidance and one retest of reported findings after your team has corrected them.

BASIC

External assessment

An external scan of one website

$390 USD

2 days · 1 revision round

  • One authorized public website in the agreed scope
  • External vulnerability scan without login
  • Review of exposed configuration and response headers
  • Finding review to flag unconfirmed scan results
  • Prioritized report with evidence and affected URLs
  • Written remediation recommendations for your team
Order this package

For applications with login

STANDARD

Authenticated web app

One web app with login and OWASP Top 10 checks

$790 USD

4 days · 1 revision round

  • One authorized web application, including login
  • Test accounts and user roles agreed before testing
  • OWASP Top 10 checks within the approved scope
  • Review of authentication, sessions and access controls
  • Evidence and severity assessment for reported findings
  • Prioritized report with remediation recommendations
Order this package

PREMIUM

Web app, API & retest

A web app and its API, with one retest

$1,490 USD

7 days · 2 revision rounds

  • Authorized assessment of one web app and its API
  • Authenticated checks across agreed roles and endpoints
  • OWASP Top 10 checks relevant to the agreed scope
  • Prioritized findings with supporting evidence
  • Fixes guidance for your development team
  • One retest of reported findings after your team's fixes
Order this package

Basic, Standard and Premium take 2, 4 and 7 days of agreed project work after authorization and access are complete. Revisions are one, one and two consolidated report-correction rounds. Premium's retest date depends on your team's fixes and is agreed at kickoff.

Multiple applications, a large API or testing restrictions? Send the target list and constraints before ordering so the assessment has a realistic boundary.

01 / FINDINGS WITH CONTEXT

TURN A FINDING
into a decision.

01

A defined testing boundary

Targets, accounts, methods and the test window are agreed in writing, so the assessment stays within your authorization.

02

Priorities your team can discuss

The report records evidence, affected locations and severity, distinguishing supported findings from unconfirmed tool output.

03

A route to follow-up

Recommendations guide your developers. Premium's single retest records the status of the reported findings after remediation.

FOR WEBSITE OWNERS, SOFTWARE TEAMS AND ORGANIZATIONS RESPONSIBLE FOR THEIR OWN SYSTEMS.

Public business websites

A focused review of the externally visible site and its exposed configuration.

Applications with user accounts

An agreed review of login, sessions and access controls using supplied test accounts.

Applications with an API

A combined app and API assessment within a defined set of endpoints and roles.

FROM AUTHORIZATION to a prioritized report.

  1. 01

    Set the rules

    Confirm ownership or authorization, exact targets, permitted methods, test accounts and a contact for the test window.

  2. 02

    Run the agreed checks

    We assess the public site or authenticated application and API according to the selected package.

  3. 03

    Review the findings

    We document supporting evidence, flag uncertainty and order remediation recommendations by priority.

  4. 04

    Deliver and close

    Your team receives the report. Premium includes one scheduled retest of reported issues after your team implements fixes.

WHAT YOU RECEIVE.

01

Assessment report

Scope, methods, limitations and prioritized findings with supporting evidence.

02

Remediation recommendations

Written next steps for your team, with more detailed fixes guidance for the app and API in Premium.

03

Retest results: Premium

The outcome of one retest of the reported findings after your developers' corrections, with unresolved items identified.

BEFORE TESTING.

  • Written permission from the owner or an authorized representative.
  • Exact domains, application URLs and API endpoints to include and exclude.
  • Test accounts for agreed roles and API documentation where relevant.
  • A test environment where available, permitted methods and a test window.
  • A technical contact, backup arrangement and constraints on sensitive data.

Authorized assessment with a clear stopping point.

This is a point-in-time vulnerability assessment, not a guarantee of security, a certification or an unrestricted penetration test. We exclude destructive tests, denial of service and unauthorized third-party systems. Your developers implement fixes; ongoing monitoring is not included. The pictured organizations and findings are illustrative fictional examples.

Before you order

QUESTIONS, ANSWERED. Before you need to ask.

How much does the assessment cost?

Basic is $390 USD for one external website scan and report. Standard is $790 for a web app with login and OWASP Top 10 checks. Premium is $1,490 for an app and API, fixes guidance and one retest.

What permission do you need?

Written authorization covering the exact systems and permitted checks. You must own the targets or have authority to approve testing. Any third-party permission needed must be in place before testing starts.

How long will it take?

The defined project work takes 2, 4 or 7 days, depending on the package, once authorization and access are complete. Premium's retest is scheduled around your developers' remediation; their work can extend elapsed time.

Do you need an administrator account?

Basic needs no login. For Standard and Premium, we agree test accounts for the relevant roles. Provide only the access required for the approved checks, preferably with test data.

Do you guarantee the website is completely secure?

No. The report describes what was assessed and found at that time. It cannot prove that every vulnerability has been found or that the website will remain secure after changes.

Will you implement the fixes?

No. These packages provide assessment and recommendations. Premium includes fixes guidance and one retest after your team implements the corrections. Code changes require a separate scope.

Is this a full penetration test?

The offer is a bounded vulnerability assessment. If a contract requires a penetration test, a named certification or particular testing methods, send the requirements before ordering so suitability can be checked.

Open chat