Skip to content
COLONFILM

SECURITY DOCUMENTATION / SOC 2 & ISO 27001

PUT YOUR SECURITY IN WRITING.
Give every policy an owner and a purpose.

A buyer asks how you manage access, vendors and incidents. Your answer should reflect how your company actually works. Our SOC 2 compliance documentation turns your practices into clear SOC 2 policies, risk records and control mappings. Need ISO 27001 policies too? Choose a coordinated pack your team can review, approve and put into use.

Packages from $790 USD

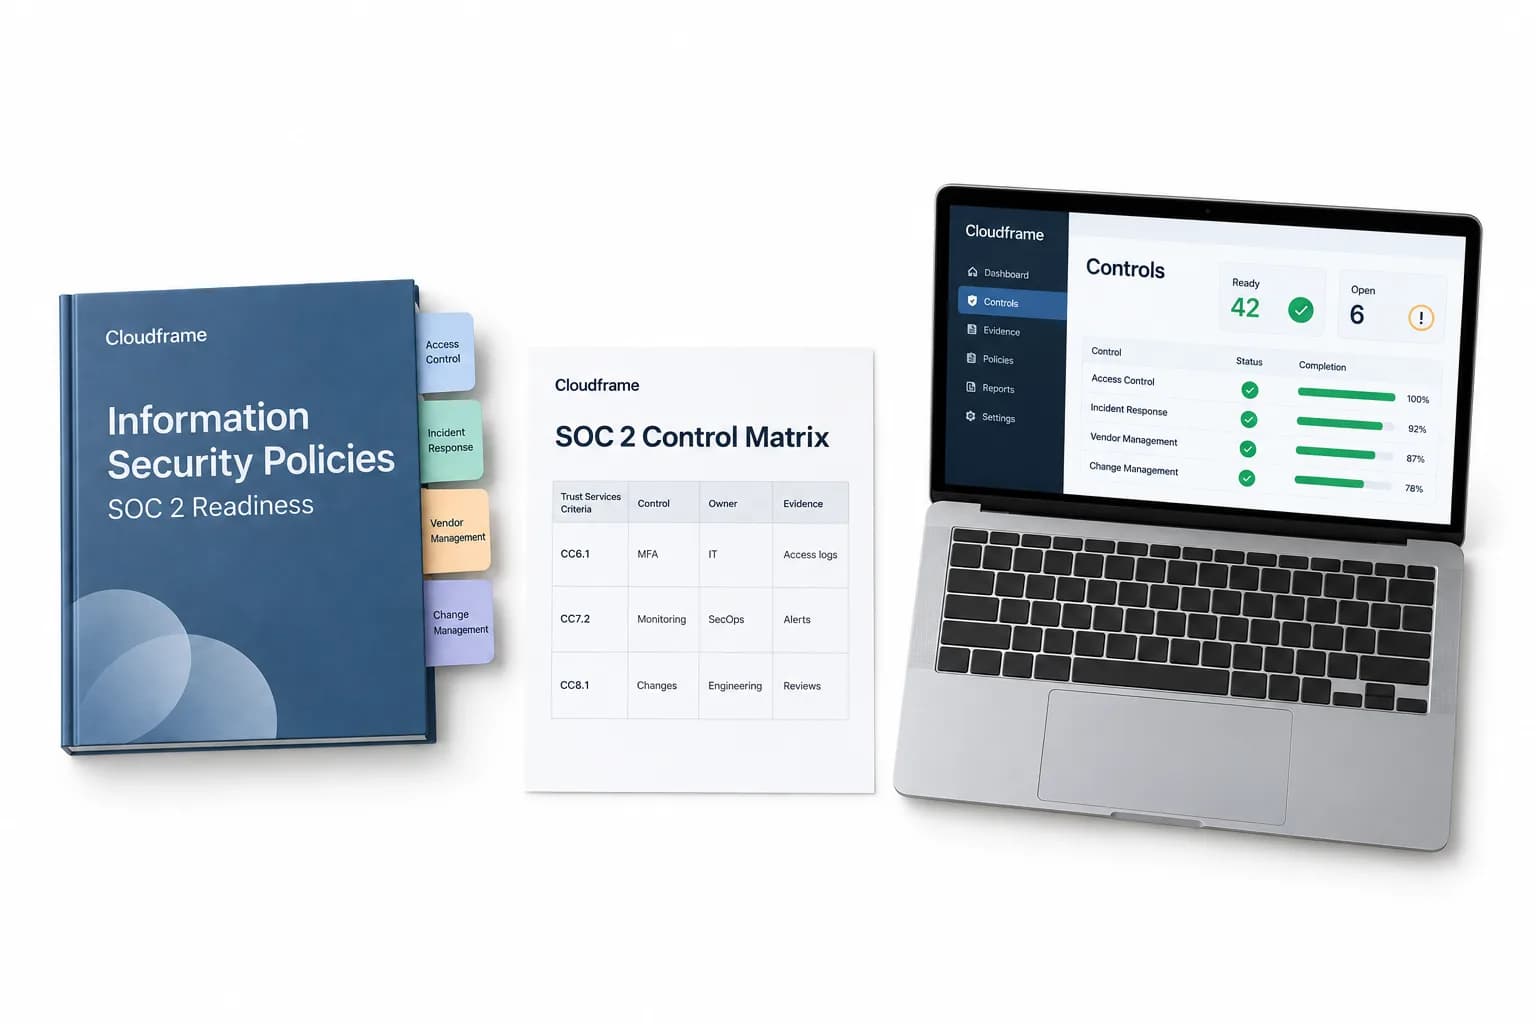
Illustrative concept: a security policy binder, a control matrix and a laptop arranged together.
AI-generated visual concept

01 / Written for your team and tools

02 / Editable policies and control records

03 / SOC 2 + ISO 27001 in Premium

AI-generated visual concepts to show possible styles, not client projects. Select an image to enlarge it.

FROM CORE POLICIES to a connected documentation set.

Basic gives you 15 tailored policies. Standard builds approximately 25 policies and procedures, a risk assessment, a register and a SOC 2 control matrix. Premium adds the ISO 27001:2022 Statement of Applicability, operational plans and a gap roadmap.

BASIC

Core policy pack

15 policies shaped around your team and tools

$790 USD

4 days · 1 revision round

  • 15 information security policies
  • Written for your stack, team and tools
  • Named policy owners and responsibilities
  • Procedures grounded in the practices you describe
  • Editable Word files for internal approval
  • Organized PDF pack for auditor review
Order this package

For SOC 2 preparation

STANDARD

SOC 2 readiness pack

Connect your policies, risks and SOC 2 controls

$1,490 USD

6 days · 1 revision round

  • Full set of approximately 25 policies and procedures
  • Documents tailored to your operating environment
  • Risk assessment with likelihood and impact
  • Editable risk register with owners and actions
  • SOC 2 control matrix mapped to Trust Services Criteria
  • Word and PDF documents plus editable register and matrix
Order this package

PREMIUM

SOC 2 + ISO 27001 pack

One coordinated documentation set for both frameworks

$2,490 USD

9 days · 2 revision rounds

  • Everything in Standard
  • ISO 27001:2022 Statement of Applicability for Annex A
  • Vendor management plan
  • Incident response plan with roles and escalation
  • Business continuity plan for agreed operations
  • Gap report with a prioritized remediation roadmap
Order this package

Basic takes 4 days, Standard 6 and Premium 9 after we accept your complete brief and system scope. They include 1, 1 and 2 consolidated revision rounds respectively.

Several entities, different operating environments or a buyer's own document list? Send the details before ordering so we can confirm the right scope.

01 / DOCUMENTS YOUR TEAM CAN USE

MAKE RESPONSIBILITIES
easy to understand.

01

Policies that fit your operation

Access reviews should name the tools and people involved. We use your setup to write responsibilities and procedures your team can recognize.

02

A traceable control story

Standard links policies to relevant Trust Services Criteria and records risks with owners and actions. Your team can follow the reasoning from requirement to document.

03

An honest picture of readiness

We distinguish current practices from proposed actions. Premium gathers the gaps into a prioritized roadmap so you can decide what to implement next.

FOR SAAS FOUNDERS, OPERATIONS LEADS AND TEAMS PREPARING SECURITY REVIEWS.

Enterprise buyer reviews

Prepare clear documents about access, data handling and suppliers when procurement asks how your business operates.

First SOC 2 preparation

Build a coherent policy set and control matrix around the system and criteria agreed for your project.

A combined SOC 2 and ISO 27001 project

Use Premium to coordinate policies, applicability decisions and operational plans across both frameworks.

FROM YOUR CURRENT PRACTICES to documents ready for review.

  1. 01

    Define the system

    Tell us what you sell, where data lives, which tools you use and who owns security decisions. Share any existing policies and reviewer requirements.

  2. 02

    Build the document map

    We agree the document list and relevant criteria, then identify missing information and the people who can confirm it.

  3. 03

    Write and cross-check

    We draft the policies and package-specific records, checking that responsibilities, terminology and control references agree.

  4. 04

    Review and take ownership

    Your team sends consolidated feedback. We deliver the revised editable files and PDFs for your internal approval and implementation.

YOUR DOCUMENTATION, READY TO HAND OVER.

01

Policies in Word and PDF

15 policies in Basic; approximately 25 policies and procedures in Standard and Premium, organized for review and future editing.

02

Risk and control records: Standard and Premium

Risk assessment, editable risk register and SOC 2 matrix mapped to the relevant Trust Services Criteria.

03

ISO and action pack: Premium

Annex A Statement of Applicability, vendor management, incident response and business continuity plans, plus a gap report and remediation roadmap.

WHAT HELPS US WRITE ACCURATE POLICIES.

  • Company overview, team roles and the system or service in scope.
  • Hosting, software, data types, locations and key suppliers.
  • Existing policies and a description of how access, incidents and backups are handled today.
  • Your intended framework, relevant criteria and any auditor or customer requests.
  • One person to confirm practices, approve changes and collect internal feedback. Share sanitized information; keep credentials out of the brief.

Documentation for the next stage.

This is preparatory documentation. A CPA firm issues the SOC 2 report; an accredited certification body handles ISO 27001 certification. Your team approves the policies, implements controls and maintains the supporting evidence.

Before you order

QUESTIONS, ANSWERED. Before you need to ask.

How much does the documentation cost?

Basic is $790 for 15 policies. Standard is $1,490 for approximately 25 policies and procedures, risk records and the SOC 2 control matrix. Premium is $2,490 and adds the ISO 27001 and operational planning documents.

How long does it take?

4, 6 or 9 days for Basic, Standard or Premium, starting when the complete brief and scope are accepted. These are document delivery times; plan your internal approvals around them.

What do you need from us?

Your system scope, team roles, tools, data flows, existing policies and a candid account of current practices. We flag missing answers and proposed controls so you can make informed decisions.

Will we receive editable documents?

Yes. Policies arrive in Word and PDF. Standard and Premium also include editable risk and control records. Premium adds the Statement of Applicability, three operational plans and the gap roadmap.

Does AI write the policies?

We use AI agents to organize inputs, draft and cross-check documents. A person reviews the work against your brief before delivery. COLONFILM is David Colón and Flor's studio in Zaragoza, Spain, designing since 2010; our Fiverr profile is Pro and Top Rated, with 1,000+ reviews and a 4.8-star rating.

Does this include the SOC 2 report or ISO 27001 certification?

The purchase covers preparatory documents. The SOC 2 examination and report belong to a CPA firm; ISO 27001 certification is handled by an accredited certification body. Their assessment and fees are separate.

What happens after delivery?

You review the files and send one consolidated revision list in Basic or Standard, or up to two in Premium. Your team then approves and maintains the documents. Future changes or new systems can be scoped as a new order.

Open chat