Skip to content
COLONFILM

APPLICATION SECURITY / AUTHORIZED PENTESTING

TEST THE RISKS THAT MATTER.
Give developers findings they can reproduce.

Can one user see another customer's records? Does an API enforce the same permissions as the app? Our penetration testing services turn an agreed test scope into verified findings, evidence and practical fixes. Start with a vulnerability assessment, choose a manual web application pentest, or test the app and API together with a remediation retest in Premium.

Packages from $490 USD

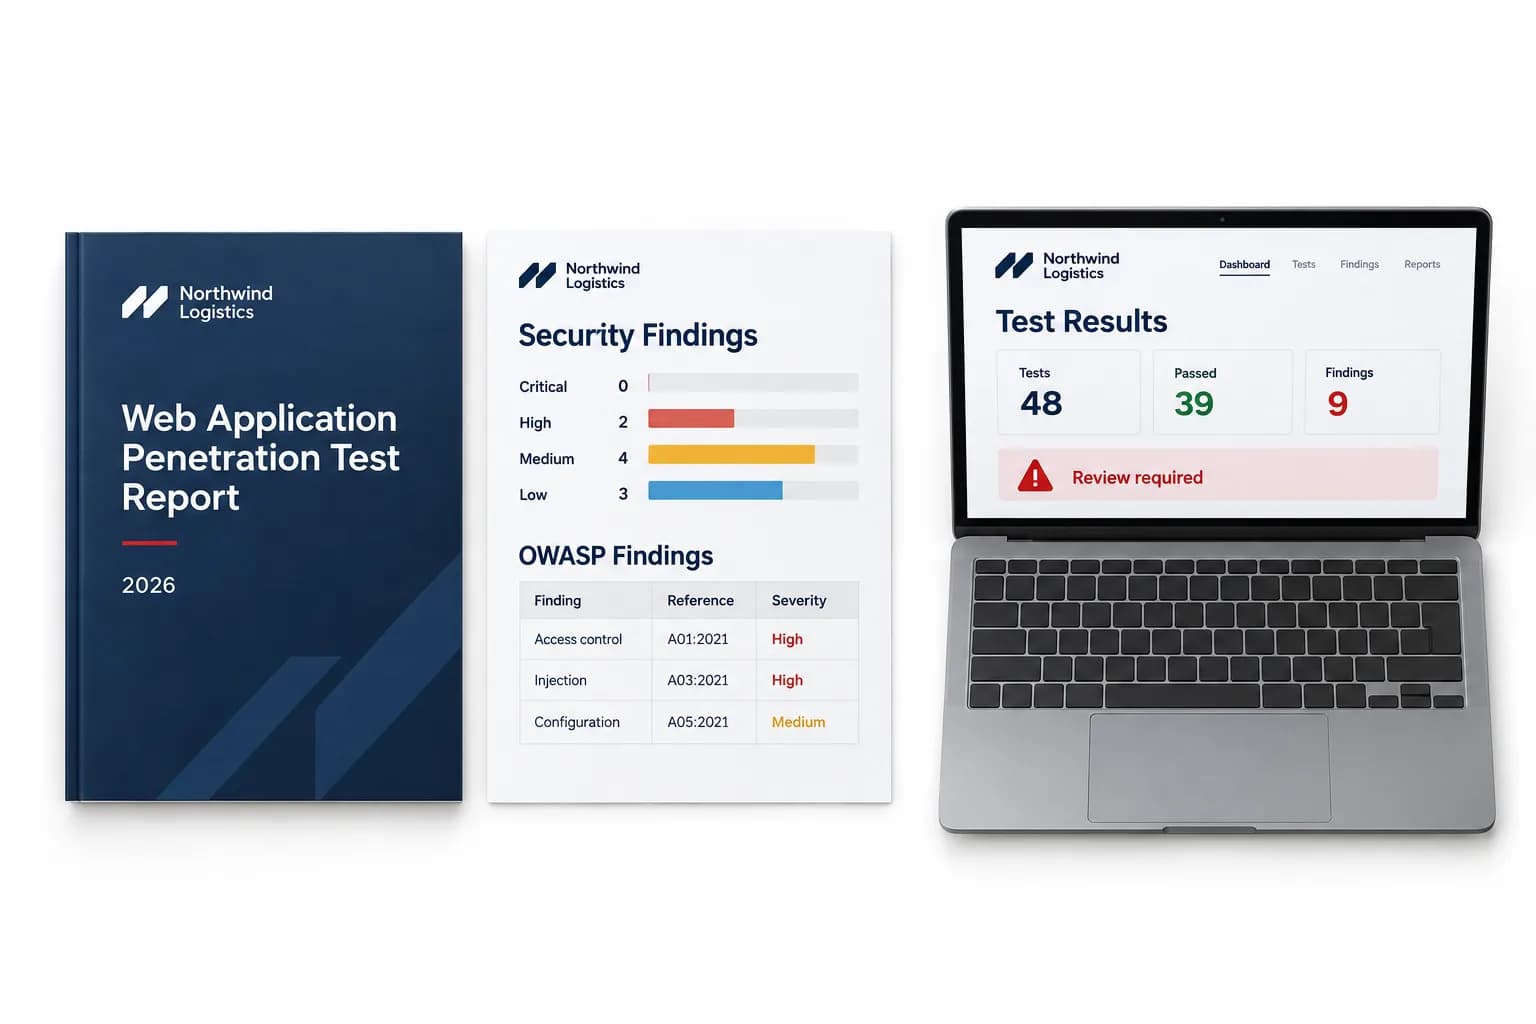
Illustrative concept: a web application pentest report beside a laptop displaying test results.
AI-generated visual concept

01 / Every reported finding verified

02 / Manual pentesting from Standard

03 / API and one retest in Premium

AI-generated visual concepts to show possible styles, not client projects. Select an image to enlarge it.

CHOOSE THE DEPTH. Get evidence your team can act on.

Basic scans one app externally and with authentication, then manually verifies every reported finding. Standard adds manual testing against OWASP Top 10 and agreed ASVS checks across up to 2 user roles. Premium adds up to 40 REST or GraphQL endpoints, business-logic tests, developer guidance and one retest within 30 days.

BASIC

Vulnerability assessment

Verified vulnerabilities in one web application

$490 USD

3 days · 1 revision round

  • One web application within an agreed scope
  • External scanning of the exposed application
  • Authenticated scanning with test accounts
  • Every reported finding manually verified
  • Risk-rated report with supporting evidence
  • Actionable fixes for each reported vulnerability
Order this package

For a manual app pentest

STANDARD

Web application pentest

Manual testing of one application and up to 2 roles

$990 USD

5 days · 1 revision round

  • Manual web application penetration test
  • Testing against OWASP Top 10 and agreed ASVS checks
  • Authenticated testing across up to 2 user roles
  • Proof-of-concept evidence for validated findings
  • Executive summary with prioritized risks
  • Technical report with reproduction steps and fixes
Order this package

PREMIUM

Web app + API pentest

Application, API and one remediation retest

$1,990 USD

8 days · 2 revision rounds

  • Everything in Standard
  • REST or GraphQL API testing: up to 40 endpoints
  • Business-logic and access-control testing
  • Remediation guidance for your developers
  • One retest within 30 days of the initial report
  • Attestation letter recording scope, dates and results
Order this package

Initial delivery takes 3, 5 or 8 days for Basic, Standard or Premium once the brief, owner-signed authorization and test access are accepted. Report revision rounds are 1, 1 and 2. Premium's separate retest takes place within 30 days of the initial report.

More than one app, more than 2 roles or over 40 API endpoints? Send the architecture and proposed scope before ordering so we can size the work.

01 / EVIDENCE BEFORE PRIORITY

KNOW WHAT WAS FOUND.
Know where to start.

01

Verified findings

Every reported vulnerability is manually checked. Each finding explains the affected component, observed behavior and risk so the report is useful beyond a scanner dashboard.

02

Context across user roles

Standard tests the agreed application with up to two roles. Premium extends the work into API permissions and business logic, such as access to another account's objects.

03

A practical remediation handover

Developers receive reproduction evidence and recommended fixes. Premium adds remediation guidance and a retest of original findings to record what has been resolved.

FOR WEB APP OWNERS AND DEVELOPMENT TEAMS PREPARING A RELEASE OR SECURITY REVIEW.

SaaS accounts and permissions

Review authenticated features and access boundaries across the roles included in the agreed application scope.

Portals and online transactions

Test the defined application flows using approved accounts and test data in the agreed environment.

Web apps backed by APIs

Use Premium to examine app and REST or GraphQL API behavior together, with up to 40 agreed endpoints.

FROM AN AUTHORIZED SCOPE to a prioritized technical report.

  1. 01

    Agree permission and scope

    Obtain written authorization signed by the system owner. We define targets, environment, test window, methods and stop conditions, preferably on staging.

  2. 02

    Test and verify

    We run the assessment or manual pentest in your package. Reported findings are checked and documented with evidence from the authorized environment.

  3. 03

    Explain the impact

    We prioritize risks and write actionable fixes. Standard and Premium include an executive summary and a technical report with proof-of-concept evidence.

  4. 04

    Review and close

    We address your consolidated report feedback. In Premium, your developers apply corrections and we perform the included retest within 30 days of the initial report.

FINDINGS FOR DECISION-MAKERS AND DEVELOPERS.

01

Risk-rated assessment report

Every package documents scope, verified findings, evidence and recommended fixes in a shareable report.

02

Executive and technical reports: Standard and Premium

A management summary plus reproduction steps, proof-of-concept evidence and remediation priorities for the development team.

03

Retest and attestation: Premium

One retest report, developer remediation guidance and a letter recording the scope, dates and results of the test.

SET UP A CLEAR TEST ENVIRONMENT.

  • Target URLs, application boundaries and an outline of the technology stack.
  • Written authorization signed by the system owner covering the system, environment and test window; staging is preferred.
  • Available test accounts and roles; share credentials securely later in the order, never in the form.
  • For Premium: API documentation and the list of up to 40 REST or GraphQL endpoints or operations agreed for testing.
  • Test data, a backup arrangement, exclusions and a contact who can stop testing if needed.

An authorized test of a defined system.

Testing requires written authorization signed by the system owner. Social engineering and denial-of-service testing are excluded. Findings describe the agreed scope at the time of testing; the report and attestation are not a certificate or a guarantee of a vulnerability-free system.

Before you order

QUESTIONS, ANSWERED. Before you need to ask.

How much do penetration testing services cost?

Basic is $490 for a verified vulnerability assessment. Standard is $990 for a manual web application pentest with up to 2 roles. Premium is $1,990 for the app plus up to 40 API endpoints, developer guidance, an attestation letter and one retest.

When will we receive the report?

In 3, 5 or 8 days for Basic, Standard or Premium after we accept the complete brief, owner-signed authorization and access. Premium's retest is a separate step within 30 days of the initial report, allowing your developers time to apply fixes.

What do you need before testing?

The owner-signed authorization, target list, environment, test window, relevant roles, test data and an incident contact. Premium also needs API documentation. Staging is preferred, and access credentials are shared securely in the order after the scope is accepted.

What will our developers receive?

Verified, risk-rated findings with evidence and recommended fixes. Standard and Premium add manual test results, proof-of-concept evidence, an executive summary and technical report. Premium includes developer guidance and the retest outcome.

Do AI agents carry out the work?

We use AI agents to support testing, analysis and reporting. A person supervises the work, manually verifies reported findings and reviews the final report. COLONFILM is David Colón and Flor's Zaragoza studio, designing since 2010, with Fiverr Pro and Top Rated status, 1,000+ reviews and a 4.8-star rating.

Does the attestation certify that our system is secure?

It records the authorized scope, dates and results. It does not certify complete security. Testing is limited to the agreed system and period, with social engineering and denial-of-service excluded.

What happens after the findings are delivered?

Your developers apply the fixes. Basic and Standard include one report revision round; Premium includes two, plus one retest of original findings within 30 days. Code implementation, extra retests and future releases can be scoped separately.

Open chat